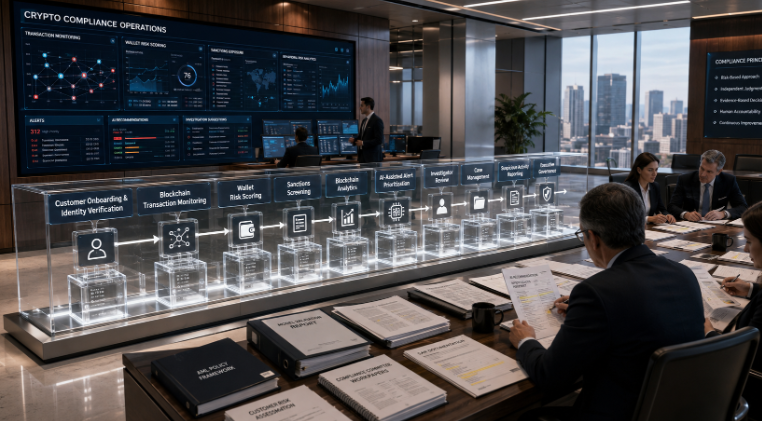
Artificial intelligence is transforming compliance at an extraordinary pace. But as automation becomes more sophisticated, one question continues to divide compliance professionals, regulators, and technology providers alike: can software eventually replace human judgment?
For many technology vendors, the answer is becoming increasingly optimistic. Artificial intelligence can summarize investigations in seconds. Blockchain analytics platforms can trace funds across thousands of wallets almost instantly. Machine learning models identify suspicious transaction patterns that traditional monitoring systems might never detect. Compliance platforms now promise faster investigations, lower operational costs, fewer false positives, and greater efficiency than ever before.
Those capabilities are impressive—and they’re changing the way crypto compliance programs operate.
But they also create an assumption that deserves closer scrutiny.
If technology can detect financial crime faster than humans, should humans still be making the decisions?
It’s an understandable question. After all, machines don’t become fatigued after reviewing hundreds of alerts. They don’t overlook transactions because they’re overwhelmed with casework. They consistently apply the same monitoring rules every time, without distraction or inconsistency.
Yet despite the remarkable advances in automation, artificial intelligence, and blockchain analytics, the answer remains no.
Not because automation isn’t effective. In fact, modern crypto compliance would be nearly impossible without it.
The real reason is that compliance has never been about simply identifying suspicious activity. It has always been about evaluating evidence, applying context, documenting reasoning, and making decisions that can withstand regulatory scrutiny. Those responsibilities still require human judgment.
Technology has become one of the compliance officer’s most valuable tools. It just hasn’t replaced the compliance officer.
Why Automation Became Essential
The cryptocurrency industry presents compliance teams with challenges that traditional financial institutions rarely encounter at the same scale.
Blockchain networks operate around the clock. Digital assets move across jurisdictions within seconds. Customers interact with decentralized exchanges, smart contracts, cross-chain bridges, and self-hosted wallets, often creating transaction histories that span multiple ecosystems before funds ever reach a centralized platform.
The sheer volume of activity makes manual monitoring unrealistic.
A growing exchange or stablecoin issuer may process hundreds of thousands—or even millions—of transactions every day. Expecting investigators to review every transaction individually would not only be inefficient; it would be impossible.
Automation emerged because the industry had no other practical option.
Today’s compliance programs rely on technology to verify customer identities, perform sanctions screening, detect suspicious transaction patterns, trace blockchain activity, calculate preliminary risk scores, and organize investigations before an analyst ever opens a case. Instead of manually collecting information from multiple systems, investigators receive organized intelligence within minutes.
That shift has fundamentally changed compliance operations.
Rather than spending the majority of their day gathering data, analysts can focus on evaluating what the data actually means. Automation has removed much of the administrative burden that once slowed investigations, allowing experienced professionals to dedicate their time to higher-value work.
This is where automation delivers its greatest benefit—not by replacing investigators, but by allowing them to investigate more effectively.
Where Crypto Compliance Automation Delivers the Greatest Value
Some compliance tasks are perfectly suited for automation because they depend on consistency rather than interpretation.
Comparing customer information against sanctions lists is one example. Monitoring transactions for predefined risk indicators is another. Blockchain analytics platforms can rapidly identify wallet clusters, trace transaction flows, and highlight exposure to illicit activity at a scale no human investigator could reasonably match.
These systems excel at processing enormous amounts of structured information quickly and consistently.
Artificial intelligence is also beginning to reshape investigative workflows. Many organizations now use AI-assisted tools to summarize lengthy blockchain investigations, organize supporting documentation, prioritize alerts based on risk, and identify behavioral patterns across historical investigations. What once required hours of manual review can often be completed in a fraction of the time.
These improvements matter because compliance teams are under constant pressure to do more with limited resources. Regulatory expectations continue to increase while transaction volumes grow alongside the industry itself.
Automation allows organizations to scale without simply adding more investigators.
But efficiency should never be confused with judgment.
Finding suspicious behavior is only one part of an investigation. Deciding what that behavior actually means—and determining the appropriate response—is something entirely different.
Technology Finds Patterns. People Understand Them.
One of the most common misconceptions surrounding artificial intelligence is that recognizing suspicious activity is the same as understanding risk.
In reality, they’re very different.
Imagine two customers who display nearly identical blockchain activity. Both frequently interact with decentralized exchanges. Both move assets across multiple wallets before transferring funds to centralized platforms. Both have indirect exposure to wallets previously associated with high-risk activity.
An automated monitoring system might assign both customers similarly elevated risk scores because their transaction behavior closely resembles known money laundering typologies.
At first glance, that conclusion seems reasonable.
But context changes everything.
One customer is a regulated institutional trading firm executing legitimate strategies on behalf of clients. The other is deliberately layering transactions through shell entities to obscure the source of illicit proceeds.
The blockchain activity may appear remarkably similar.
The risk does not.
This is where experienced investigators create value. They understand business purpose, customer relationships, expected transaction behavior, geographic exposure, licensing status, and commercial context. They recognize when a blockchain pattern has an innocent explanation—and when it deserves immediate escalation.
Technology identifies anomalies.
People determine whether those anomalies actually represent financial crime.
That distinction remains one of the most important principles in modern compliance.
The Danger of Trusting Automation Too Much
Ironically, one of automation’s greatest strengths can also become one of its biggest weaknesses.
As technology becomes more accurate, people naturally begin trusting it more.
This phenomenon, often referred to as automation bias, occurs when investigators place too much confidence in automated recommendations instead of independently evaluating the underlying evidence.
At first, the shift is subtle.
An investigator notices that the monitoring system is usually correct, so they begin relying more heavily on its conclusions. Over time, they spend less effort challenging risk scores or reviewing why an alert was generated. Instead of forming an independent opinion, they begin looking for information that supports the software’s recommendation.
Critical thinking gradually gives way to confirmation.
When that happens, technology stops assisting judgment and starts replacing it.
The consequences can be significant.
False positives continue because nobody questions outdated monitoring rules. False negatives remain undetected because investigators assume the system would have identified them if they were important. AI-generated summaries become accepted without verification. Risk scores slowly evolve into conclusions rather than starting points for further investigation.
None of these failures occur because the software is inherently flawed.
They occur because human oversight quietly disappears.
Technology performs exactly as it was designed. The governance surrounding it does not.
Why Explainability Matters More Than Accuracy
As artificial intelligence becomes more sophisticated, compliance programs face a challenge that extends well beyond efficiency.
Can the technology explain why it reached its conclusion?
For years, transaction monitoring systems relied on clearly defined rules. If a customer exceeded a certain threshold, interacted with a sanctioned jurisdiction, or triggered a predefined scenario, investigators could easily understand why an alert appeared. Even if those rules generated too many false positives, the underlying logic remained transparent.
Artificial intelligence changes that equation.
Many modern AI models identify suspicious activity by recognizing patterns across enormous datasets rather than following straightforward rules. They may correctly identify high-risk behavior that traditional monitoring systems would miss, but they don’t always make their reasoning obvious. Their recommendations are based on statistical relationships that can be difficult for investigators (and even developers) to fully explain.
That creates a governance challenge.
If a regulator asks why a customer received a high-risk score, “the AI recommended it” is not an acceptable answer, nor should it be. Organizations must still demonstrate how decisions were reached, how models are validated, and how investigators review automated recommendations before acting on them.
Explainability has become just as important as accuracy.
The goal isn’t simply to build systems that identify more suspicious activity. It’s to build systems whose conclusions can be understood, challenged, documented, and defended during regulatory examinations.
Compliance decisions cannot become a black box.
Human Judgment Extends Beyond Blockchain Data
One of the biggest limitations of automation is that compliance investigations rarely begin and end with blockchain analytics.
Tracing digital assets is only one part of understanding financial crime risk.
Experienced investigators naturally combine blockchain intelligence with information gathered from customer onboarding, business profiles, transaction history, source-of-funds documentation, adverse media, geographic exposure, law enforcement requests, and ongoing customer communications. Looking at any one of those sources in isolation can produce an incomplete, and sometimes misleading, picture.
Consider a customer whose wallet receives funds that can be traced back to a sanctioned entity several transactions earlier.
A blockchain analytics platform immediately flags the exposure, and rightly so. The connection deserves attention.
But an experienced investigator doesn’t stop there.
They evaluate how direct the exposure actually was. They review whether the customer knowingly interacted with the sanctioned wallet or whether the exposure occurred through several layers of intermediary transactions. They compare the activity against the customer’s expected behavior, review prior account activity, and determine whether additional due diligence is warranted before escalating the case.
That additional context often determines whether the activity represents meaningful financial crime risk or simply an incidental blockchain interaction.
Without human analysis, both situations might receive exactly the same treatment.
With human judgment, investigators can distinguish between technical exposure and genuine risk.
That’s an important difference because compliance isn’t about identifying every possible concern. It’s about responding appropriately to the concerns that actually matter.
The Regulatory Standard Hasn’t Changed
The technology supporting compliance has evolved dramatically over the past decade.
Regulatory expectations have evolved as well.
What hasn’t changed is who remains accountable.
Whether an organization relies on traditional transaction monitoring software, sophisticated blockchain analytics, or the latest AI-powered compliance platform, regulators continue evaluating the effectiveness of the compliance program as a whole, not simply the technology behind it.
During examinations, reviewers are less interested in impressive software demonstrations than they are in understanding how that technology is governed.
How are monitoring rules developed?
Who validates AI models before deployment?
How often are alert thresholds reviewed?
Can investigators override automated recommendations?
What quality assurance processes exist to identify false positives and false negatives?
Who ultimately approves high-risk decisions?
These questions all point toward the same conclusion.
Technology is only one component of an effective compliance program.
Strong governance remains equally important.
Organizations sometimes assume that implementing more advanced technology automatically strengthens compliance. In reality, sophisticated tools without appropriate oversight can introduce entirely new risks.
Imagine an AI model that successfully reduces false positives by 40%. On paper, the improvement looks impressive. Investigators become more efficient, alert volumes decline, and operational costs decrease.
Months later, however, an internal validation review discovers that the model consistently deprioritized a specific money laundering typology because historical training data contained too few examples.
The software functioned exactly as designed.
The governance surrounding the software failed to identify the blind spot.
That distinction matters because regulators are not evaluating whether technology is perfect. They are evaluating whether organizations understand its limitations and have built controls to manage them.
Where Crypto Compliance Is Heading Next
The conversation surrounding artificial intelligence often suggests that organizations must eventually choose between automation and human expertise.
The future is far more likely to involve both.
Automation will continue taking over repetitive, data-intensive tasks that computers naturally perform better than people. Artificial intelligence will become increasingly capable of identifying emerging typologies, organizing investigations, summarizing evidence, and highlighting unusual customer behavior before analysts ever begin their review.
Meanwhile, the role of compliance professionals will continue evolving.
Instead of spending hours manually tracing blockchain transactions or assembling case files, investigators will spend more time evaluating context, validating automated findings, interviewing customers, assessing regulatory implications, and documenting the reasoning behind complex decisions.
In other words, technology will change how compliance professionals work—not whether they are needed.
This evolution also changes the skills organizations should value.
Future investigators will need to understand blockchain analytics, artificial intelligence, and emerging technologies, but they will also need strong analytical thinking, professional skepticism, communication skills, and sound judgment. They will be responsible not only for investigating suspicious activity but also for overseeing the technologies designed to detect it.
As compliance programs become more technologically advanced, human expertise becomes more, not less, valuable.
Crypto Compliance Automation Is Most Effective With Humans in the Loop
Perhaps the biggest misconception surrounding automation is that success should be measured by how many people it replaces.
A better measure is how much better it allows people to perform.
The strongest compliance programs are not eliminating investigators. They’re giving those investigators better information, faster access to evidence, and more time to analyze meaningful risks instead of performing repetitive administrative work.
That’s a fundamentally different objective.
Automation should reduce friction, improve consistency, and increase efficiency. It should identify relationships that humans might miss and organize information in ways that support faster, better-informed investigations.
What it should never do is become the final decision-maker.
Every meaningful compliance decision still requires accountability. Someone must decide whether suspicious activity warrants escalation, whether a customer relationship remains acceptable, whether enhanced due diligence is necessary, or whether a Suspicious Activity Report (SAR) should be filed. Those decisions carry regulatory, legal, operational, and reputational consequences that extend far beyond the capabilities of any algorithm.
Technology can recommend.
Technology can prioritize.
Technology can accelerate.
But responsibility cannot be automated.
Conclusion
Automation has fundamentally reshaped crypto compliance, and that transformation is only accelerating. Artificial intelligence, blockchain analytics, automated transaction monitoring, and intelligent case management systems have made compliance programs faster, more scalable, and significantly more effective than they were just a few years ago. Organizations that ignore these technologies risk falling behind both operationally and competitively.
At the same time, the industry’s enthusiasm for automation should not obscure a simple reality.
Compliance has never been about processing data alone. It is about exercising judgment.
Technology can identify suspicious patterns across millions of blockchain transactions. It can uncover hidden wallet relationships, detect sanctions exposure, summarize investigations, and surface risks that might otherwise remain unnoticed.
What it cannot do is understand the full context behind every customer relationship, balance competing risks, defend a decision during a regulatory examination, or accept accountability for the outcome.
Those responsibilities still belong to people.
The organizations that build the strongest compliance programs over the next decade will not be those pursuing fully autonomous compliance. They will be the firms that recognize automation for what it truly is: an extraordinarily powerful tool that strengthens human expertise rather than replacing it.
Because the future of crypto compliance isn’t about choosing between technology and people.
It’s about ensuring each one is doing what it does best.
Build a Smarter Crypto Compliance Automation Strategy
Crypto compliance automation can significantly improve efficiency, consistency, and scalability—but it cannot replace sound judgment, governance, and accountability. As firms continue adopting AI and automated compliance technologies, regulators will increasingly expect organizations to demonstrate that automation enhances, rather than replaces, effective risk management and human oversight.
Evaluating or expanding your crypto compliance automation capabilities? BitAML helps cryptocurrency businesses, stablecoin issuers, fintechs, banks, and payment companies design, assess, and optimize compliance programs that effectively integrate automation while meeting AML, sanctions, fraud, consumer protection, and regulatory expectations. Contact us today to discuss how we can help your organization build a resilient, future-ready compliance program.